Banking Technology & Cybersecurity: Real-World Engineering
Fraud systems, payments engineering, banking malware, and what building secure financial technology looks like inside one of Africas largest retail banks.
Scammernomics: How Banks Fight Fraud by Attacking Money Mule Economics
1. Fraud in context: the fraud to market share ratio Fraud numbers mean very little in isolation, because the bank with the most complaints against it is usually just the bank with the most customers, and the only honest way to read the figures is to set them against size. The comparison worth making is […]
Read more →
Hidden Bank Fees Exposed: How AI Will End Fee Smuggling
There is nowhere left to hide. For decades, banks built an elegant asymmetry into the relationship with their customers. The bank had a team of specialists, the time to design products, and the lawyers to draft disclosure documents that were technically correct and practically unreadable. The customer had a life to live and, at the […]
Read more →
The South African Banking Paradox: Abundance, Consolidation, and the Coming Reckoning
These thoughts are my own and I am often wrong, so don’t get too excited if you disagree with me. South Africa is experiencing a banking paradox. Consumers have never had more choice, with digital challenger banks, retailer backed banks, insurer led banks, and mobile first offerings launching at a remarkable pace, while at the […]
Read more →
hping3 Penetration Testing on macOS: 10 Techniques
⚠️ LEGAL DISCLAIMER AND TERMS OF USE **READ THIS CAREFULLY BEFORE PROCEEDING** Legal Requirements: **AUTHORIZATION REQUIRED**: You MUST have explicit written permission from the system owner before running any of these tests **ILLEGAL WITHOUT PERMISSION**: Unauthorized network scanning, port scanning, or DoS testing is illegal in most jurisdictions **YOUR RESPONSIBILITY**: You are solely responsible for […]
Read more →
Cloudflare Free Tier Review: Why It Works for Enterprise
By Andrew Baker, CIO at Capitec Bank There is a truth that most technology vendors either do not understand or choose to ignore: the best sales pitch you will ever make is letting someone use your product for free. Not a watered-down demo, not a 14-day trial that expires before anyone has figured out the […]
Read more →
Capitec Secure Safe and Why a Duress PIN Makes You Less Safe, Not More
1. The problem we are actually solving South Africa’s crime problem has quietly become a banking problem. Criminals no longer need to hack a banking app, they force victims to unlock it themselves. The industry calls this transfer mugging, and it is growing fast. Express kidnappings, where a victim is grabbed and forced to open […]
Read more →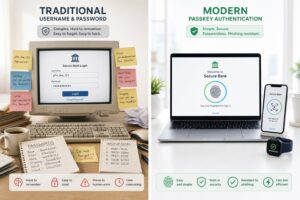
Passkeys in Banking, Part 1: What They Actually Fix, and What They Quietly Don’t
Passkeys are the most consequential change to consumer authentication in twenty years, and they are also being oversold, because the gap between the marketing and the implementation detail is exactly where fraud losses will land. The industry framing is simple enough. Public key cryptography replaces the shared secret, so there is nothing to phish, nothing […]
Read more →
ShedLock and Payments: Every Way It Can Fail, How to Retry Safely, and Every Lock Type Worth Knowing
1. What ShedLock Is and How It Works Spring Boot makes it trivial to schedule a task. You add @EnableScheduling to a configuration class, annotate a method with @Scheduled, and the framework fires it on your chosen cron or interval. The problem surfaces the moment you deploy more than one instance of your application. In […]
Read more →
How Banks Can Break Client Hypnosis: Contextual Authorisation and the Fight Against Social Engineering Fraud
by Andrew Baker 1. Opening: The Client Has Been Captured The fraud victim approving a transaction they believe is a refund is not making a mistake. They are not confused or careless or naive. They are operating under full psychological capture, executing instructions from an authority figure they have been conditioned over the course of […]
Read more →Scan SSL/TLS Ciphers With nmap and sslscan on macOS
To retrieve a list of the SSL/TLS cipher suites a particular website offers you can either use sslscan or nmap alternatively you can just use nmap (note: i use “-e en0” to bypass zscaler): Another variant (including cert dates, again “-e en0” is used to bypass zscaler):
Read more →SYN Flood Testing With hping3: Parallel Processes Guide
A SYN flood test using hping3 that allows you to specify the number of SYN packets to send and scales horizontally with a specific number of processes can be created using a Bash script with the xargs command. This approach allows you to distribute the workload across multiple processes for better performance. The Script This […]
Read more →NMAP + Claude MCP: 20 Vulnerability Scans on macOS
Introduction NMAP (Network Mapper) is one of the most powerful and versatile network scanning tools available for security professionals, system administrators, and ethical hackers. When combined with Claude through the Model Context Protocol (MCP), it becomes an even more powerful tool, allowing you to leverage AI to intelligently analyze scan results, suggest scanning strategies, and […]
Read more →