Banking Technology & Cybersecurity: Real-World Engineering
Fraud systems, payments engineering, banking malware, and what building secure financial technology looks like inside one of Africas largest retail banks.
macOS Passive Domain Vulnerability Scanner: Full Guide
Below is a fairly comprehensive passive penetration testing script with vulnerability scanning, API testing, and detailed reporting. Features Installation Required Dependencies Optional Dependencies Usage Basic Syntax Options Examples: Network Configuration Default Interface: en0 (bypasses Zscaler) To change the interface, edit line 24: The script automatically falls back to default routing if the interface is unavailable. Debug Mode […]
Read more →
Passkeys in Banking, Part 2: Securing Passkey Enrolment with Browser Registration
This is the second of two articles. Part one, Passkeys in Banking: What They Actually Fix, and What They Quietly Don’t, sets out the benefits and the risks. This part addresses what a bank can do about the risk that matters most. In short. A passkey is a strong credential, and the strength of a […]
Read more →Protected: Neo by Capitec: AI Client Support That Resolves Issues Proactively
There is no excerpt because this is a protected post.
Read more →
Card Payment Authentication and the Intent Problem: Why Identity, Consent and Authorization Are Not the Same Thing
1. Card Payment Authentication, Consent and Authorization Are Three Different Things 1.1 Who Actually Does What in a Card Payment Because this argument turns on some fine distinctions, it is worth spending a moment on who does what, since the vocabulary of card payments is unhelpfully opaque and the same word often means different things […]
Read more →SCP Files to EC2: Mac & Linux Command Guide
I always forget the syntax of SCP and so this is a short article with a simple example of how to SCP a file from your laptop to your EC2 instance and how to copy it back from EC2 to your laptop: Copying from Laptop to EC2 scp -i identity_file.pem source_file.extention username@public_ipv4_dns:/remote_path scp: Secure copy protocol-i: Identity […]
Read more →
Debit Orders: Who Gets to Take Money From Your Account, What You Can Do About It, and What Your Bank Can and Cannot Do
I should apologise up front for the length of this article. Every section answers a question real people are asking, and the length is a fair reflection of how much clients are expected to work out on their own, usually just after money has left their account. You don’t need to read all of it. […]
Read more →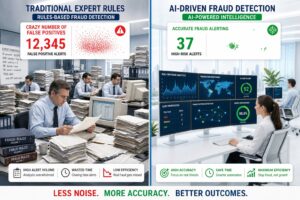
Finally, an AI That Understands Money, Part Three: Teaching It What Is Out of Character
Abnormal is always relative. An embedding computed in advance can hold an inbound payment before it arrives, and the same property explains where this approach fails. This is the last of three parts. Part one explains what Revolut’s PRAGMA is and how it works. Part two covers credit and financial inclusion. Where the first two […]
Read more →
Decoys as Zero Day Sensors: Deception, Isolation and Early Signal
Most of the security stack we buy is built to recognise things that have already been seen somewhere else, which is exactly why it struggles with zero days: a signature cannot exist for an exploit nobody has catalogued, a patch cannot exist for a flaw the vendor does not know about, and an anomaly model […]
Read more →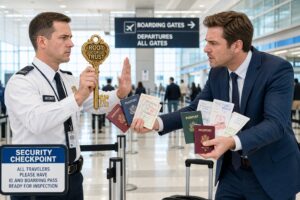
Root of Trust: Fix the Business Process Before You Bypass the Security
Picture a business process that reaches the point where a customer must approve something important, where the intended control is an approval through their banking app, but the app has not yet been activated. Someone suggests sending an SMS instead so that the process can continue, and in the moment this sounds like a perfectly […]
Read more →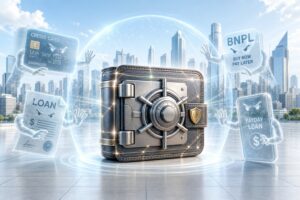
One Wallet, One Premium: Rebuilding Credit Around the Client Instead of the Product
There is an asymmetry sitting in plain sight in every retail lending book, and once you notice it you cannot unsee it. Some of the smallest, shortest and most frequently repaid advances we write exhibit extraordinarily low losses, particularly where repayment is tied closely to the customer’s income stream, and yet almost the entire architecture […]
Read more →