AWS, Cloud & Database Architecture
Banking-grade AWS deployments, multi-cloud trade-offs, and database design at scale. The architectural decisions that prevent 3am incidents.
Delete 50+ EBS Snapshots Using AWS CLI: Step-by-Step
The Amazon EC2 console allows you to delete up to 50 Amazon Elastic Block Store (Amazon EBS) snapshots at once. To delete more than 50 snapshots, use the AWS Command Line Interface (AWS CLI) or the AWS SDK. To see all the snapshots that you own in a specific region, run the following. Note, replace […]
Read more →
AWS CLI: ZSP: Keeping AWS Keys Out of Plaintext on Your Mac
A free, open source macOS tool that takes long lived AWS keys out of ~/.aws, seals them with the Secure Enclave, and asks for Touch ID before any of them is used. Open a terminal on almost any developer’s Mac and type cat ~/.aws/credentials. Mine printed three AWS access keys and secrets in plain text. […]
Read more →How to Backup MySQL on Bitnami WordPress to S3
I recently managed to explode my wordpress site (whilst trying to upgrade PHP). Anyway, luckily I had created an AMI a month ago – but I had written a few articles since then and so wanted to avoid rewriting them. So below is a method to create a backup of your wordpress mysql database to […]
Read more →Protected: Neo by Capitec: AI Client Support That Resolves Issues Proactively
There is no excerpt because this is a protected post.
Read more →TPC-H Test Data for AWS Redshift and EMR: Setup Guide
If you need to test out your big data tools below is a useful set of scripts that I have used in the past for aws emr and redshift the below might be helpful:
Read more →Auto-Recover a Failed WordPress Instance on AWS
When WordPress goes down on your AWS instance, waiting for manual intervention means downtime and lost revenue. Here are two robust approaches to automatically detect and recover from WordPress failures. Approach 1: Lambda Based Intelligent Recovery This approach tries the least disruptive fix first (restarting services) before escalating to a full instance reboot. Step 1: […]
Read more →SCP Files to EC2: Mac & Linux Command Guide
I always forget the syntax of SCP and so this is a short article with a simple example of how to SCP a file from your laptop to your EC2 instance and how to copy it back from EC2 to your laptop: Copying from Laptop to EC2 scp -i identity_file.pem source_file.extention username@public_ipv4_dns:/remote_path scp: Secure copy protocol-i: Identity […]
Read more →AWS Error Messages, API Standards & Region Defaults: Fix Needed
This is a short blog, and its actually just simple a plea to AWS. Please can you do three things? North Virginia appears to be the AWS master node. Having this region as a master region causes a large number of support issues (for example S3, KMS, Cloudfront, ACM all use this pet region and […]
Read more →
Replacing NFS With S3 Without Changing Your Code: Automating Amazon S3 Files
For most of S3’s life, the honest answer to “can I just mount a bucket and point my application at it?” was some version of “sort of, if you are willing to live with FUSE and its compromises.” Tools like s3fs and Mountpoint for Amazon S3 gave you a path that looked like a directory, […]
Read more →Auto-Renew Let’s Encrypt Certs on Linux with Cron
If you want to automatically renew your certs then the easiest way is to setup a cron just to call letsencrypt periodically. Below is an example cron job: First create the bash script to renew the certificate Now enter the script in the following format into nano: Now edit the crontab to run the renew […]
Read more →Public Cloud Migration: Why Lift-and-Shift Strategies Fail
The cloud is hot…. not just a little hot, but smokin hot!! Covid is messing with the economy, customers are battling financially, the macro economic outlook is problematic, vendor costs are high and climbing and security needs more investment every year. What on earth do we do??!! I know…. lets start a crusade – lets […]
Read more →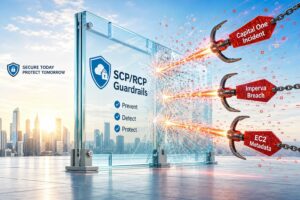
AWS Security for Banks: SCPs, RCPs and Declarative Policies Against Real Incidents
September 18, 2026 · Andrew Baker 1. Why central guardrails, not guidelines Most public AWS breaches are not exotic. They are the same handful of mistakes recurring across different companies, and the fix in nearly every case was available beforehand as a preventive control rather than a detective one. The Capital One breach of 2019 […]
Read more →